 Book a Demo
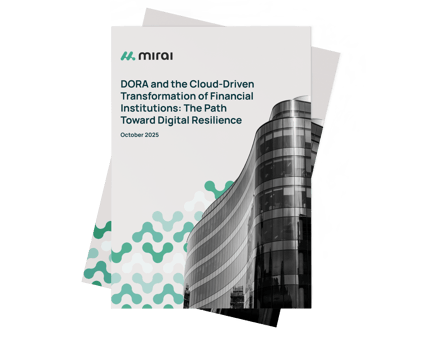
A practitioner guide for CISOs, risk managers, and cloud architects navigating DORA's requirements for operational resilience and third-party governance.
What Is DORA and Why Does It Matter for Financial Institutions?
The Digital Operational Resilience Act (DORA), adopted in 2022 and enforced from January 2025, marks a turning point for the European financial sector. For the first time, a single regulatory framework unifies fragmented ICT risk management rules—replacing overlapping national and sector-specific standards with one coherent set of obligations that applies equally to financial institutions and their third-party technology providers.
DORA's premise is realistic rather than pessimistic: incidents are inevitable. What matters is whether institutions can respond, recover, and maintain trust. The regulation formalizes a mindset shift; resilience is no longer a reactive measure but a measurable, enforceable operational capability.
In practice, DORA affects three interconnected dimensions:
-
Risk management must now extend beyond internal systems to cover the entire supply chain, including fourth-party providers.
-
Organizational governance must evolve, with cross-functional coordination among risk, compliance, and IT functions approved by the board.
-
And technological infrastructure must support rapid recovery, continuous monitoring, and documented exit strategies, requirements that cloud-native environments are uniquely positioned to meet.
This whitepaper explores how migrating from on-premises infrastructure to cloud environments reshapes DORA compliance and how resilience-by-design becomes both a regulatory obligation and a competitive advantage.
Whitepaper Key Findings
-
DORA unifies fragmented regulation. One enforceable framework that replaces the overlapping EBA, ECB, NIS Directive, and national rules, effective January 2025.
-
Cloud accelerates DORA compliance. Integrated security controls, automated disaster recovery, and continuous monitoring, difficult and costly to replicate on-premises.
-
Third-party risk extends to fourth parties. A vulnerability in a subcontractor's code is the institution's regulatory responsibility.
-
Vendor lock-in is a DORA risk. Documented, tested exit strategies for every critical cloud provider are a binding obligation.
-
Resilience by design replaces compliance by audit. DORA requires resilience to be embedded in infrastructure, contracts, and culture from the outset.
Fill out the form to access your copy and discover how your institution can build readiness for the cloud era of digital resilience under DORA.
What Does This Whitepaper Cover?
A Complete Guide to Cloud Resilience Under DORA
- The Foundation of DORA
Origins, regulatory context, and how it unifies the European financial ecosystem - Reinforcing Risk Management in the Digital Era
ICT risk, third-party and supply chain governance under DORA - Organizational Impact
Governance restructuring, vendor management, and resilience as an operational discipline - Cultural Shift and Resilience by Design
Embedding continuity into processes, not bolting it on after - Technological Transformation
The shift from on-premises to cloud-native infrastructure - On-Premise vs Cloud
A structured comparison of capabilities, risks, and trade-offs - The Cloud as Both Facilitator and Challenge
Vendor lock-in, exit strategies, and multicloud considerations - Final Reflections
The path from fragmented compliance to integrated digital resilience
Who Should Read This?
CISOs and cybersecurity executives navigating DORA's technical requirements
Risk and compliance leaders managing ICT governance and third-party oversight
Cloud and infrastructure architects designing DORA-compliant environments
Financial operations and IT governance teams are preparing for regulatory audits
Digital transformation and regulatory strategy professionals in European financial institutions